Public-to-private transitions
Lobby layouts and staff doors can expose routes into protected spaces.

FINANCIAL FACILITIES / PHYSICAL SECURITY
Test the physical safeguards protecting staff, customers and sensitive financial operations.
Financial institutions operate across public lobbies, employee-only spaces, service areas and controlled operational rooms. Risks can emerge where customer traffic intersects with staff access, where branch procedures vary by location, or where security technology does not reflect daily practice. Phantom PenTest reviews these pathways and recommends practical improvements.
OPERATIONAL REALITIES
Risk looks different at every facility. These are the practical conditions our assessment considers in banks.
Lobby layouts and staff doors can expose routes into protected spaces.
Similar locations may operate different opening, closing and visitor procedures.
Handling areas and staff movement require dependable separation and oversight.
A control may be technically installed but ineffective when notification and action are unclear.
WHAT WE ASSESS
We evaluate how physical barriers, technology, procedures and people work together. Scope is agreed in advance, testing is controlled, and findings are focused on exposures that matter to the facility.
Reduce entry-point ambiguity in environments built around both public service and restricted operations.
Lobby boundaries, staff doors and controlled access between public and private zones.
Physical access procedures and layered restrictions where authorized.
Badge issuance, revocation, escorts and temporary service access.
Procedures, after-hours access and escalation arrangements.
Practical visibility, detection gaps and guard response coordination.
Consistency of policy, post orders and physical controls across facilities.
ILLUSTRATIVE TEST SCENARIO
Authorized. Controlled. Operationally aware.An authorized engagement may test whether a person using ordinary public access routes can reach employee-only areas, while avoiding interference with customers, cash operations and safety systems.
PHANTOM'S METHODOLOGY
We combine assessment, evidence and leadership-ready reporting—without treating every property like the same facility.
Confirm objectives, authorized areas, exclusions, safety limitations and the decisions your team needs to make.
Review site controls and procedures; perform controlled physical penetration testing only where expressly permitted.
Organize supporting evidence, identify probable consequences and recommend realistic remediation actions.
OUR PROPRIETARY ADVANTAGE
A New Dimension in Physical Security. Developed exclusively by Phantom PenTest, Penetrate360 connects branch layouts, secure areas, employee access points and protective measures in a visual assessment of your security. Understand how separate gaps could combine into real exposure, and prioritize changes that strengthen protection where it matters most.
Discover the Penetrate360 Advantage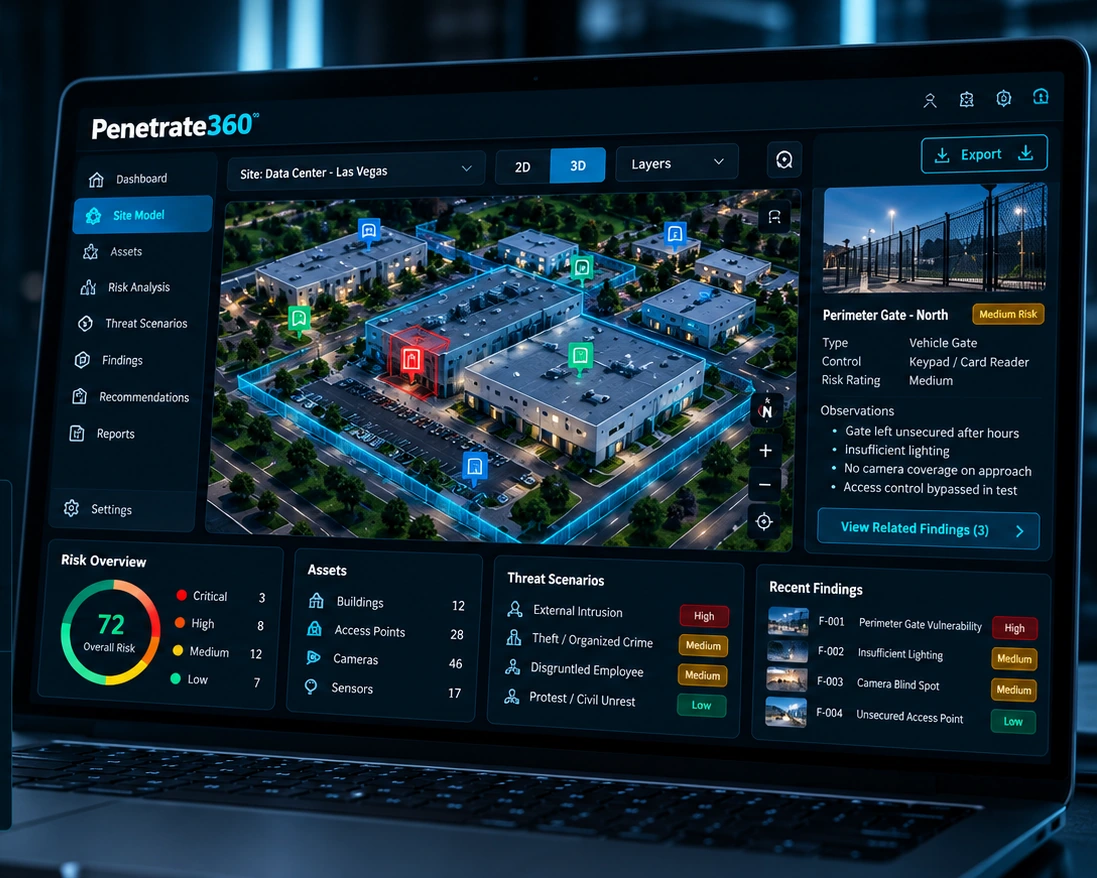
WHAT YOUR ORGANIZATION RECEIVES
Leadership gets an assessment built for decisions, not a folder of unprioritized observations.
An accessible overview of the security exposures that deserve attention.
A discussion of key findings, operating constraints and improvement priorities.
Supporting observations, evidence and recommendations organized by risk.
Sequenced next steps to strengthen the facility's physical security posture.
COMMON QUESTIONS
Start with a defined scope. We'll help determine which parts of the environment merit the closest review.
Yes. A consistent framework can identify site-specific findings while showing recurring patterns across a branch portfolio.
Only within a defined, authorized scope that protects employees, customers and business operations. Sensitive handling areas may be excluded or assessed through observation and review.
No. Findings support security improvement and risk discussions, but our engagements are not presented as regulatory certification or an audit opinion.
DISCUSS YOUR FACILITY
Talk with Phantom PenTest about a professionally scoped, authorized physical security assessment for your banks environment.