Contractor & vendor access
Temporary credentials, shared entrances and unfamiliar personnel can weaken established access protocols.
CRITICAL INFRASTRUCTURE / PHYSICAL SECURITY
Protect high-availability operations by testing the security controls that govern physical access to critical infrastructure.
Data centers depend on more than uptime technology. A single weak delivery entrance, uncontrolled contractor credential, or gap between perimeter and interior controls can undermine an otherwise sophisticated security program. Phantom PenTest examines the practical ways people, processes, and physical systems interact across your facility.
OPERATIONAL REALITIES
Risk looks different at every facility. These are the practical conditions our assessment considers in data centers.
Temporary credentials, shared entrances and unfamiliar personnel can weaken established access protocols.
A secure fence is not enough if loading bays, mechanical areas or secondary doors create alternate paths.
Badge readers and interlocks depend on real-world behavior, door hardware and reliable alarm response.
Cameras, alarms and post orders must support a coordinated response during routine and high-pressure operations.
WHAT WE ASSESS
We evaluate how physical barriers, technology, procedures and people work together. Scope is agreed in advance, testing is controlled, and findings are focused on exposures that matter to the facility.
Protect every layer of the facility — from site perimeter to critical rooms.
Fence line, gates, guard operations and approaches to controlled zones.
Badge permissions, visitor onboarding, interlocks, mantraps and anti-tailgating measures.
Server halls, network rooms, security operations areas and high-consequence spaces.
Receiving, escorts, temporary badges and off-hours access.
Coverage, alarms, monitoring routines and potential blind spots.
How security teams verify, communicate and respond to security events.
ILLUSTRATIVE TEST SCENARIO
Authorized. Controlled. Operationally aware.An authorized test may examine whether a visitor or contractor can move beyond approved zones despite layered access controls, with activities carefully scoped to avoid interfering with live operations.
PHANTOM'S METHODOLOGY
We combine assessment, evidence and leadership-ready reporting—without treating every property like the same facility.
Confirm objectives, authorized areas, exclusions, safety limitations and the decisions your team needs to make.
Review site controls and procedures; perform controlled physical penetration testing only where expressly permitted.
Organize supporting evidence, identify probable consequences and recommend realistic remediation actions.
OUR PROPRIETARY ADVANTAGE
A New Dimension in Physical Security. Developed exclusively by Phantom PenTest, Penetrate360 transforms site layouts, perimeter defenses, restricted access points and security systems into a clearer picture of data center risk. See how vulnerabilities could connect, what they might mean for critical operations, and where improvements can make the greatest difference.
Discover the Penetrate360 Advantage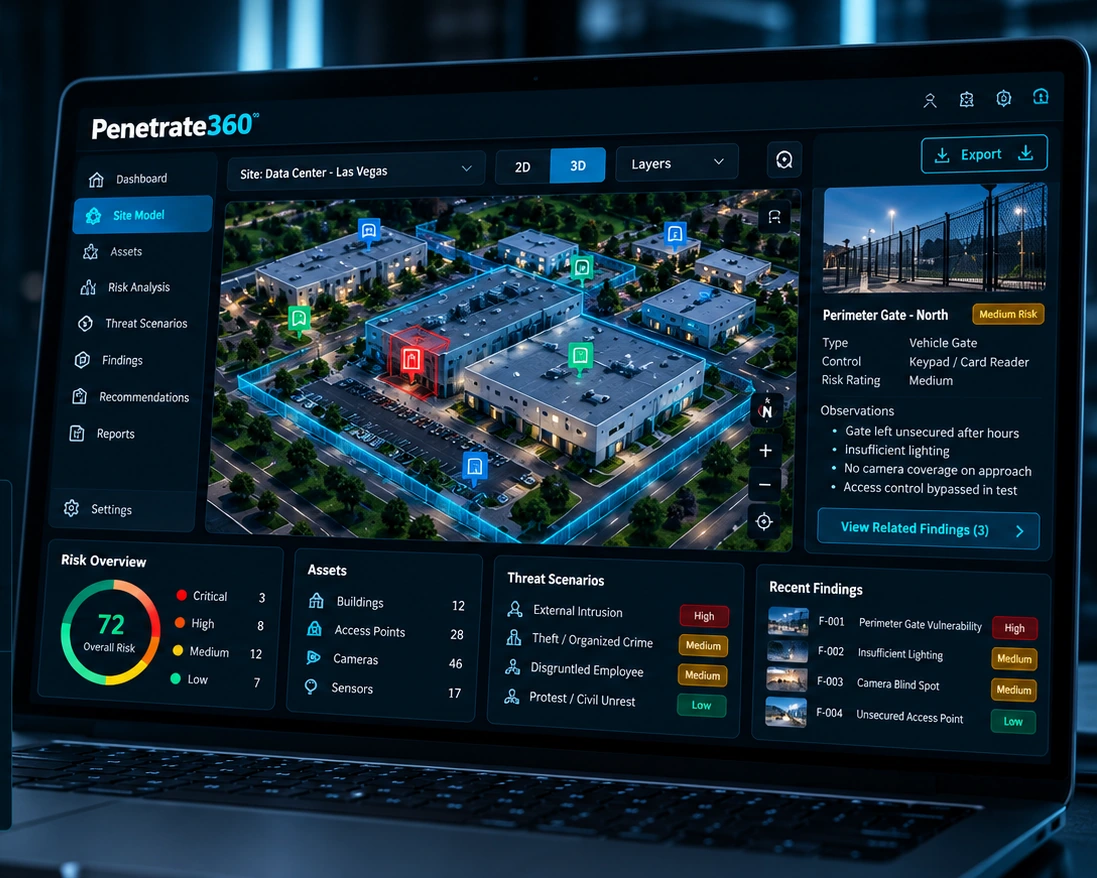
WHAT YOUR ORGANIZATION RECEIVES
Leadership gets an assessment built for decisions, not a folder of unprioritized observations.
An accessible overview of the security exposures that deserve attention.
A discussion of key findings, operating constraints and improvement priorities.
Supporting observations, evidence and recommendations organized by risk.
Sequenced next steps to strengthen the facility's physical security posture.
COMMON QUESTIONS
Start with a defined scope. We'll help determine which parts of the environment merit the closest review.
Yes. The assessment scope, permitted hours, exclusions, safety requirements and escalation contacts are agreed before work begins. Tests are designed around operational continuity.
Yes. We evaluate how access points, permissions, human behavior and monitoring procedures work together; any controlled testing is explicitly authorized.
No. Phantom PenTest focuses on physical security controls, personnel procedures and authorized physical penetration testing—not network or application testing.
DISCUSS YOUR FACILITY
Talk with Phantom PenTest about a professionally scoped, authorized physical security assessment for your data centers environment.